📦 Marketplace status: Submitted to Splunkbase (app 9875) — pending approval (Splunk review, up to 5 business days). Meanwhile, install the
.tar.gzfrom Releases.
SOC ingestion for Darkmoon AI pentest results over the HTTP Event Collector, plus an
offensive-validation loop that triggers a Darkmoon retest/campaign straight from a Splunk
correlation search. Ships CIM-aligned sourcetypes, six SOC dashboards, and a hard-secured
Send to Darkmoon alert action.
Privacy by design. Events carry safe metadata only — campaign/finding ids, severity, status, target reference, MITRE, technology and timestamps. Evidence, secrets, credentials, tokens and request/response bodies are never ingested. A defense-in-depth index-time redaction also strips token-like strings.
App id darkmoon · content type Splunk App · version 1.0.0 · MIT.
Darkmoon is open-source — a star really helps us grow.
🌐 Website: dark-moon.org · 📚 Docs: docs.dark-moon.org · ⭐ Star the core: github.com/ASCIT31/Dark-Moon
Install the integrations, right where you work:
| Platform | Get it |
|---|---|
| VS Code | VS Code Marketplace |
| JetBrains | JetBrains Marketplace |
| GitHub Actions | GitHub Marketplace |
| GitLab CI/CD | CI/CD Catalog |
| Jenkins | Download the .hpi |
| Client & CLI | npm: @darkmoon_ai/client |
Captured from a real Splunk Docker instance running this app against the synthetic
Demo Shop dataset (zeroed secrets, demo-shop.local). No evidence, endpoints or tokens.
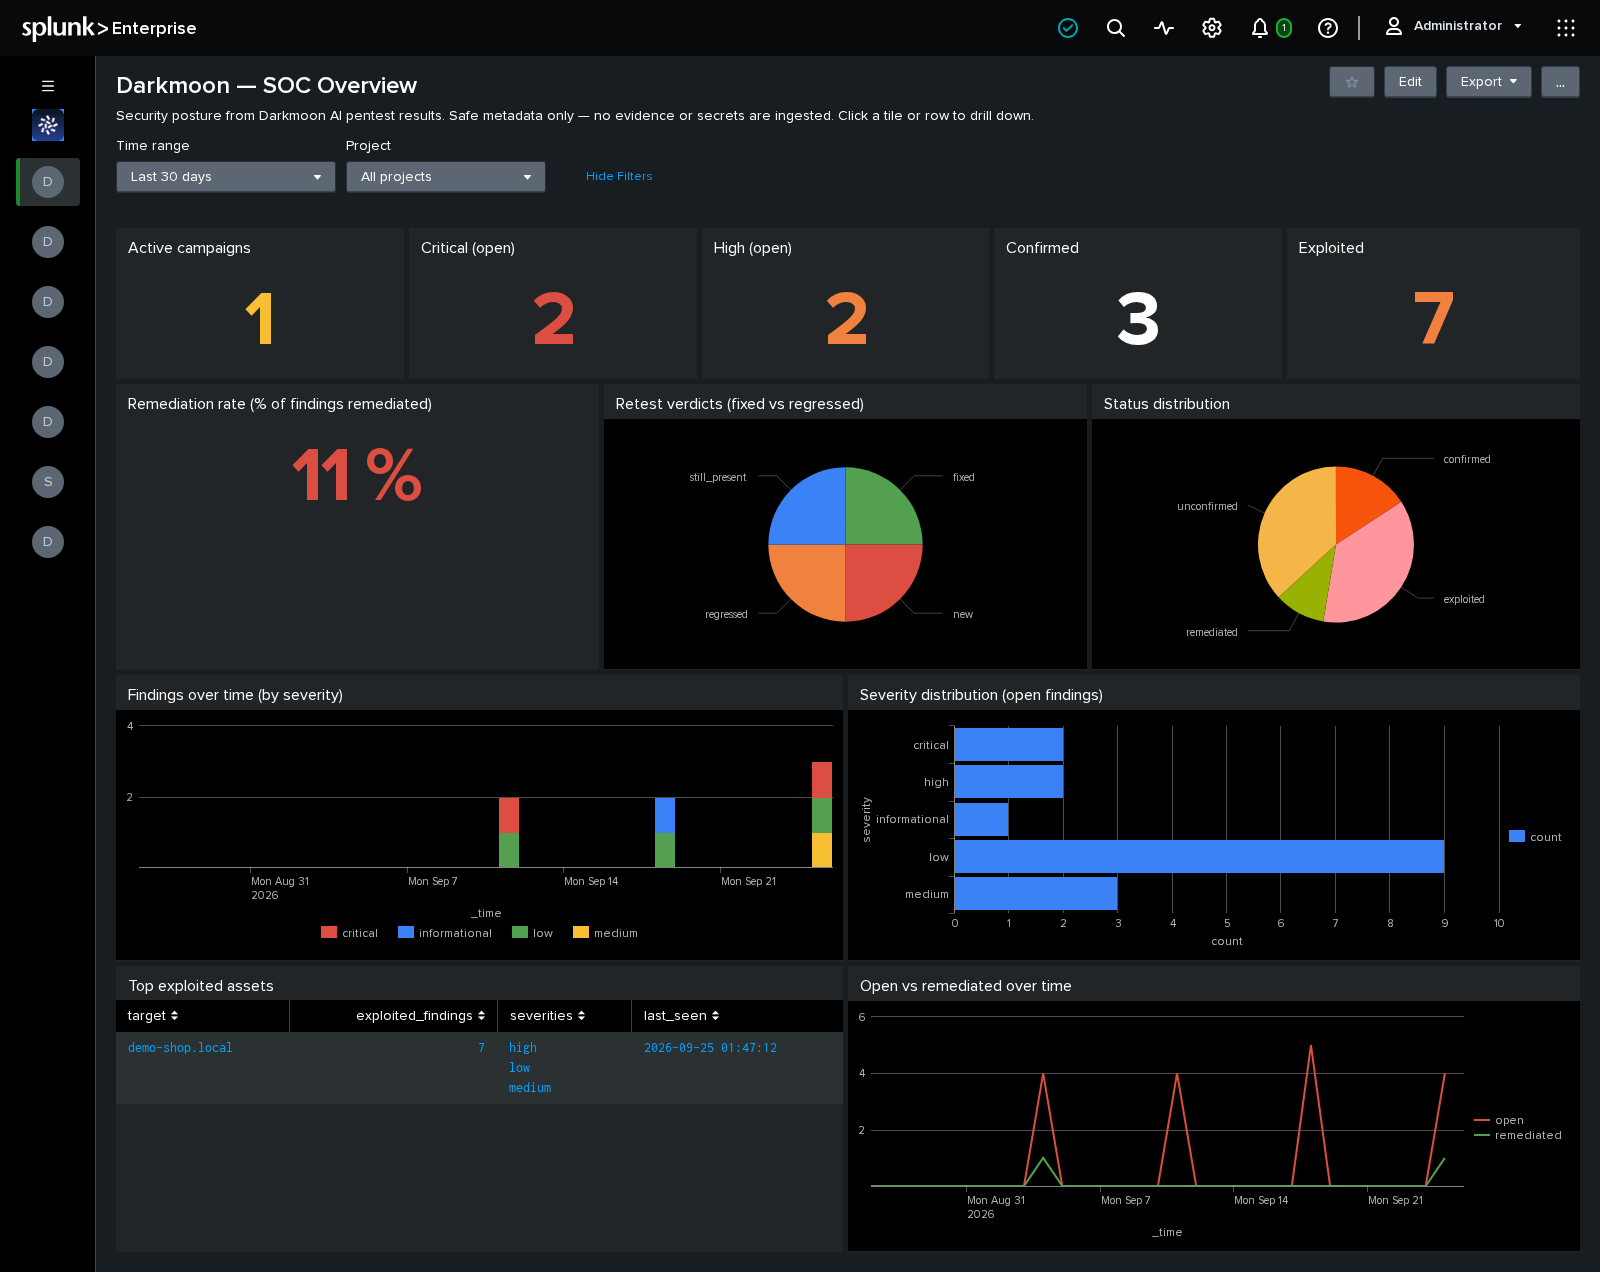
SOC Overview — posture KPIs (active campaigns, critical/high, confirmed, exploited, remediation rate), findings over time, severity/status distributions, top exploited assets:
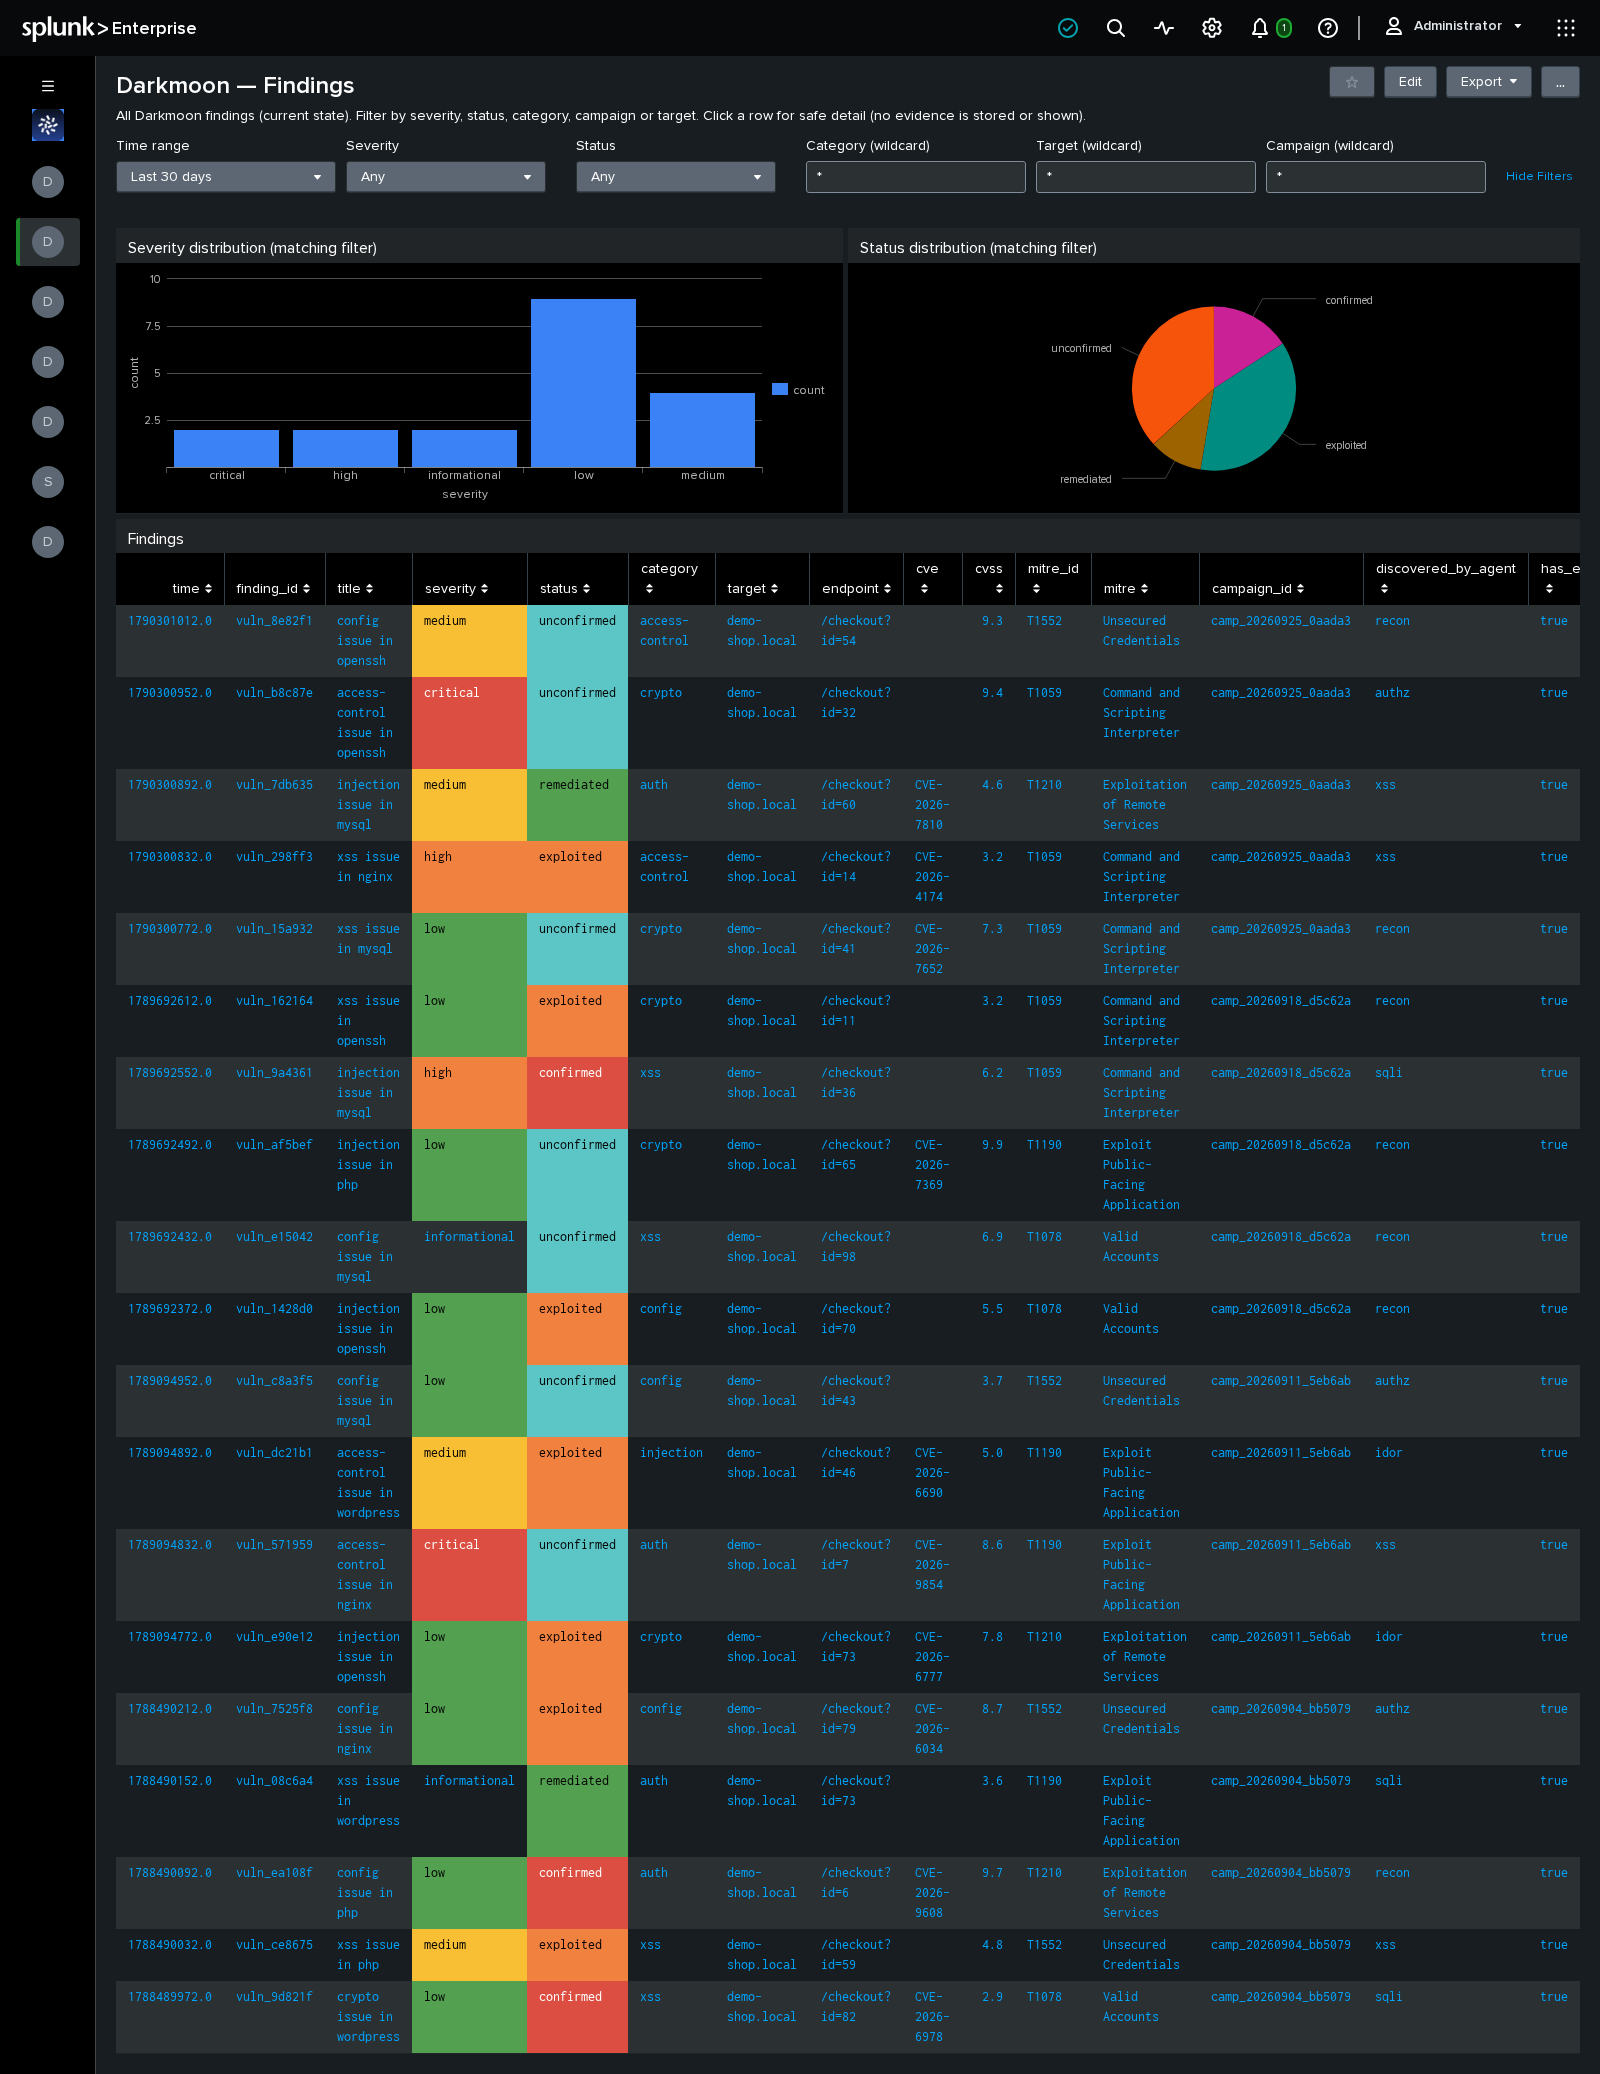
Findings — every finding with severity/status/category/target/campaign filters and safe detail:
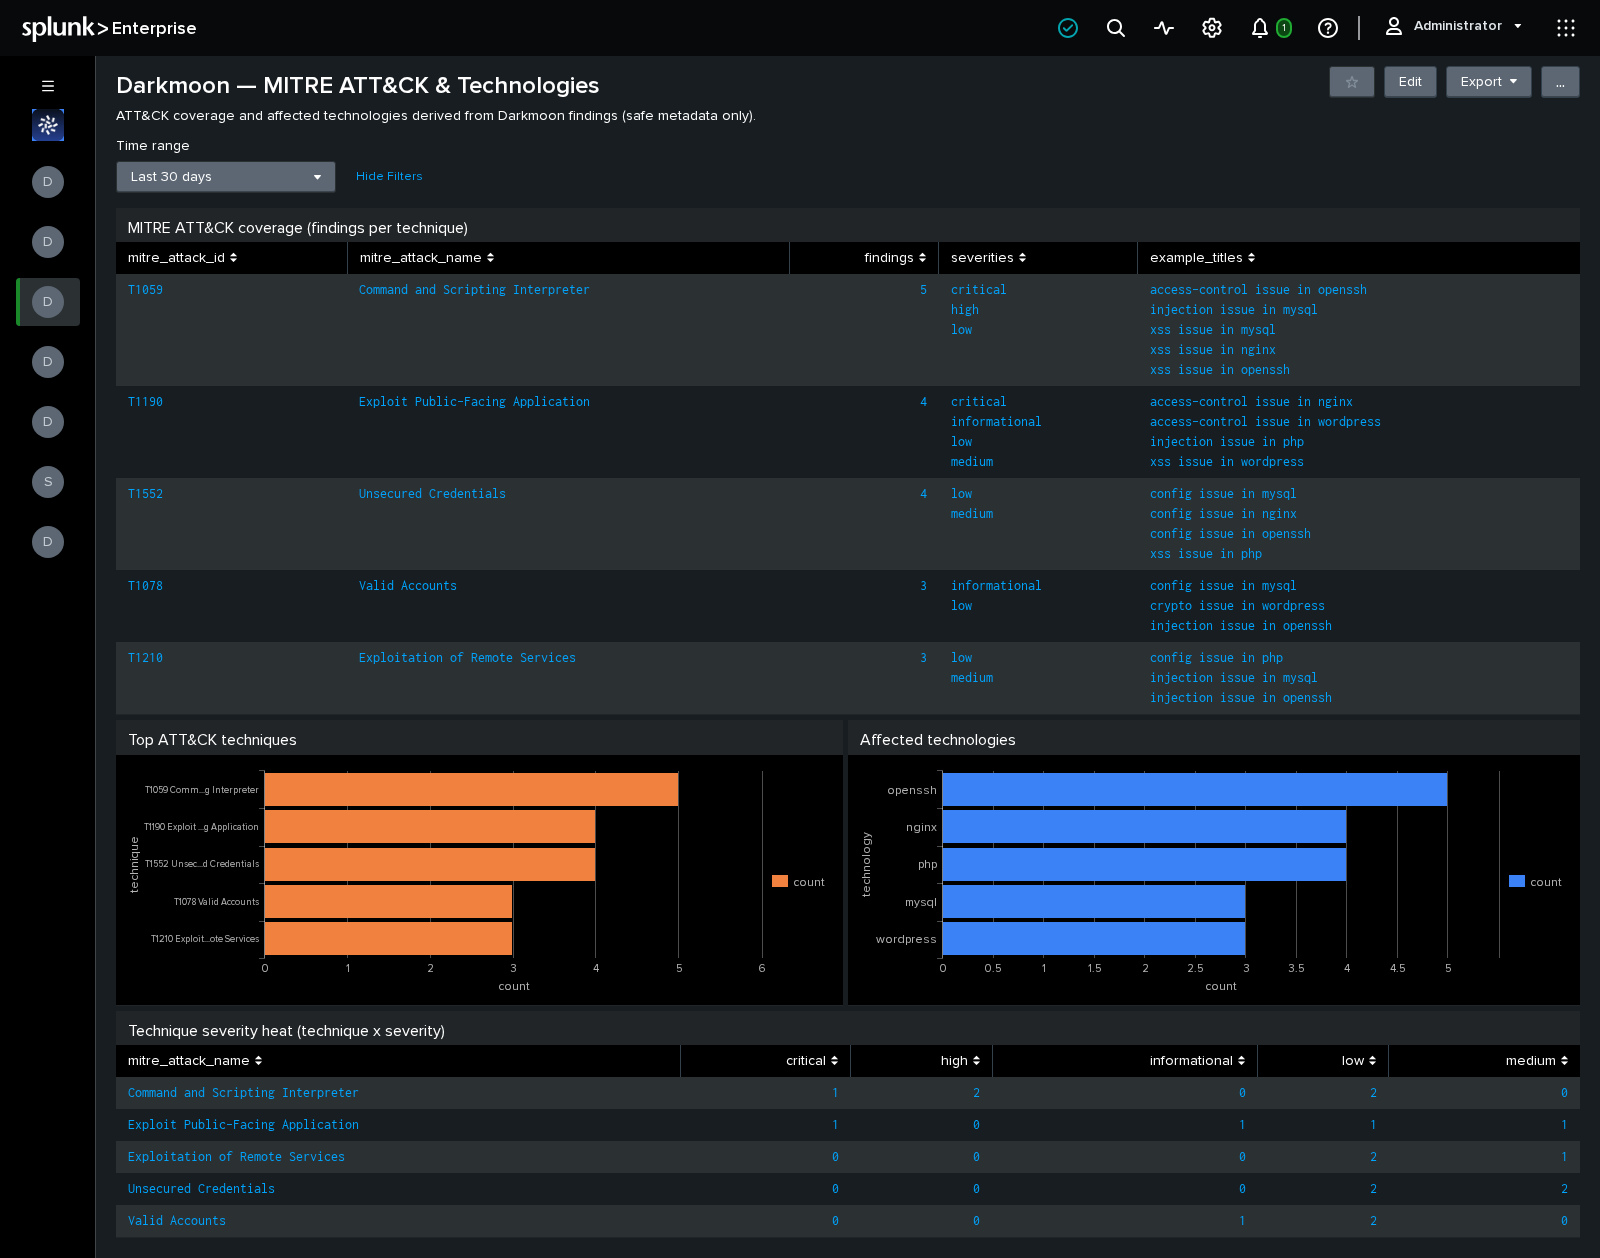
MITRE ATT&CK & Technologies — technique coverage, top techniques, affected technologies:
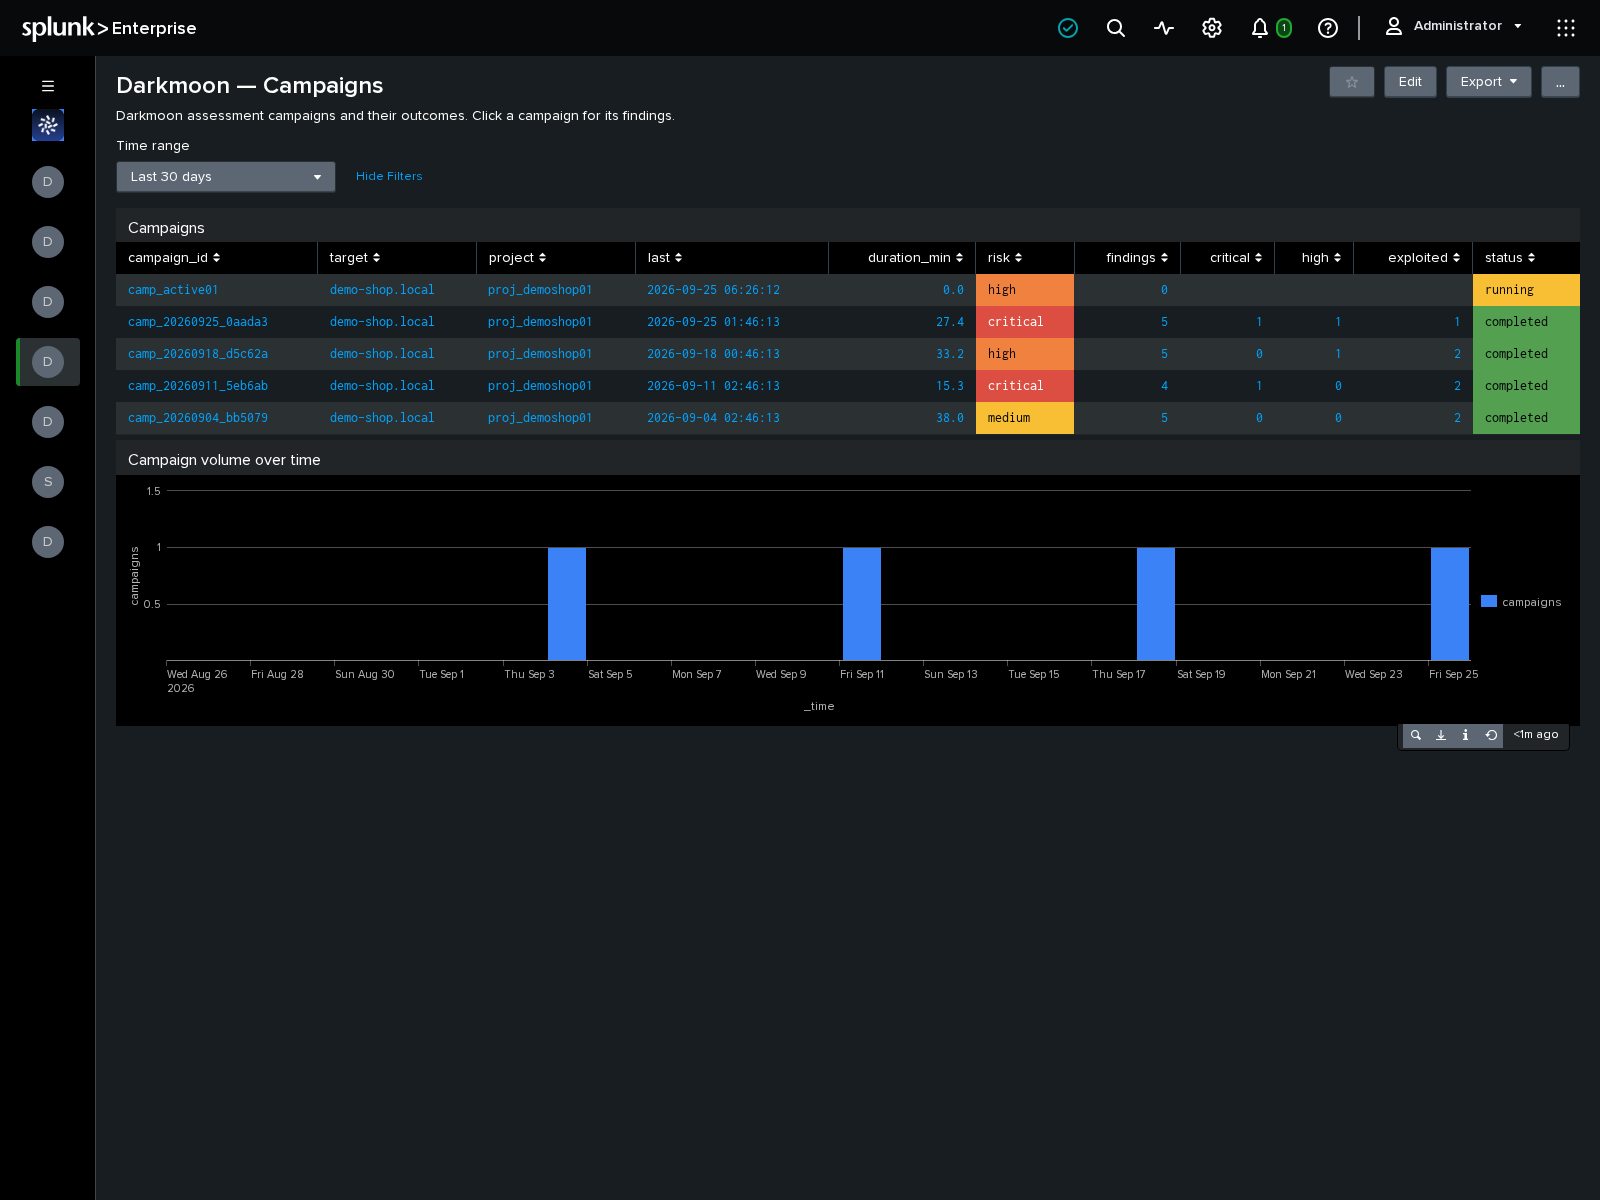
Campaigns — assessment campaigns, outcomes and drill-down to findings:
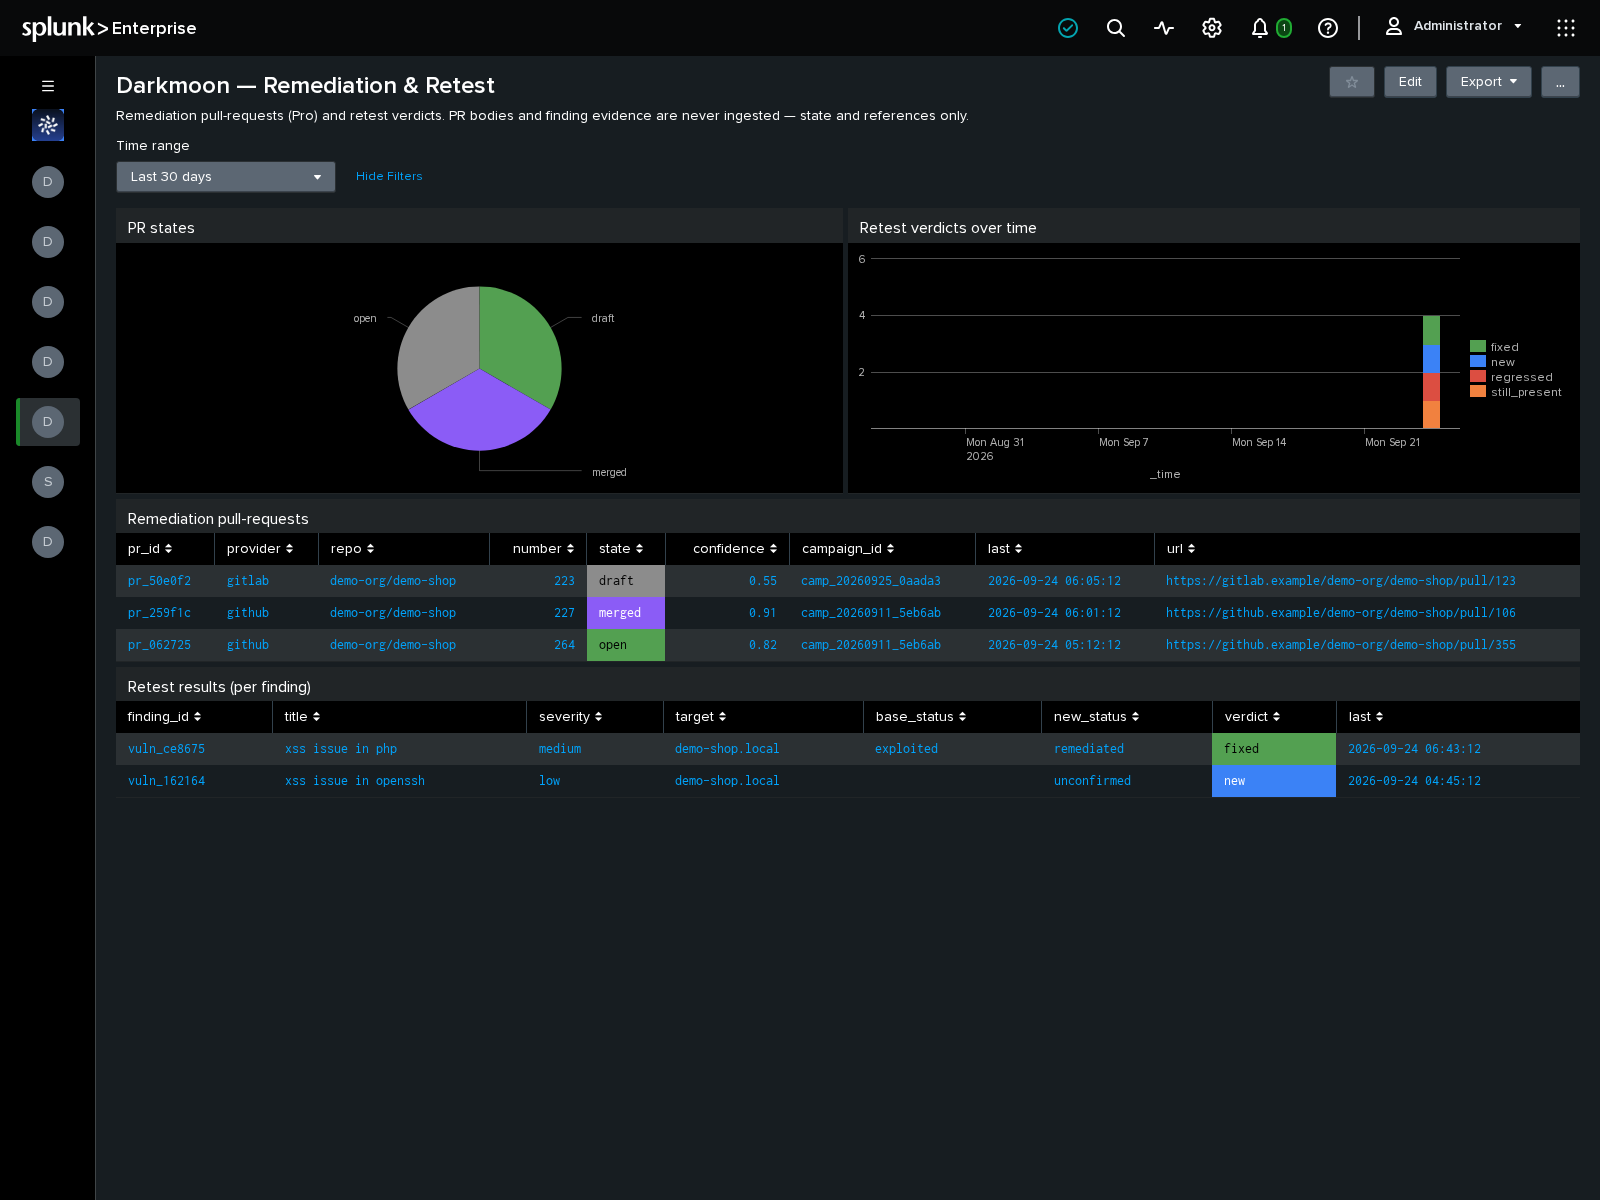
Remediation & Retest — PR states and retest verdicts (fixed / regressed / still_present / new):
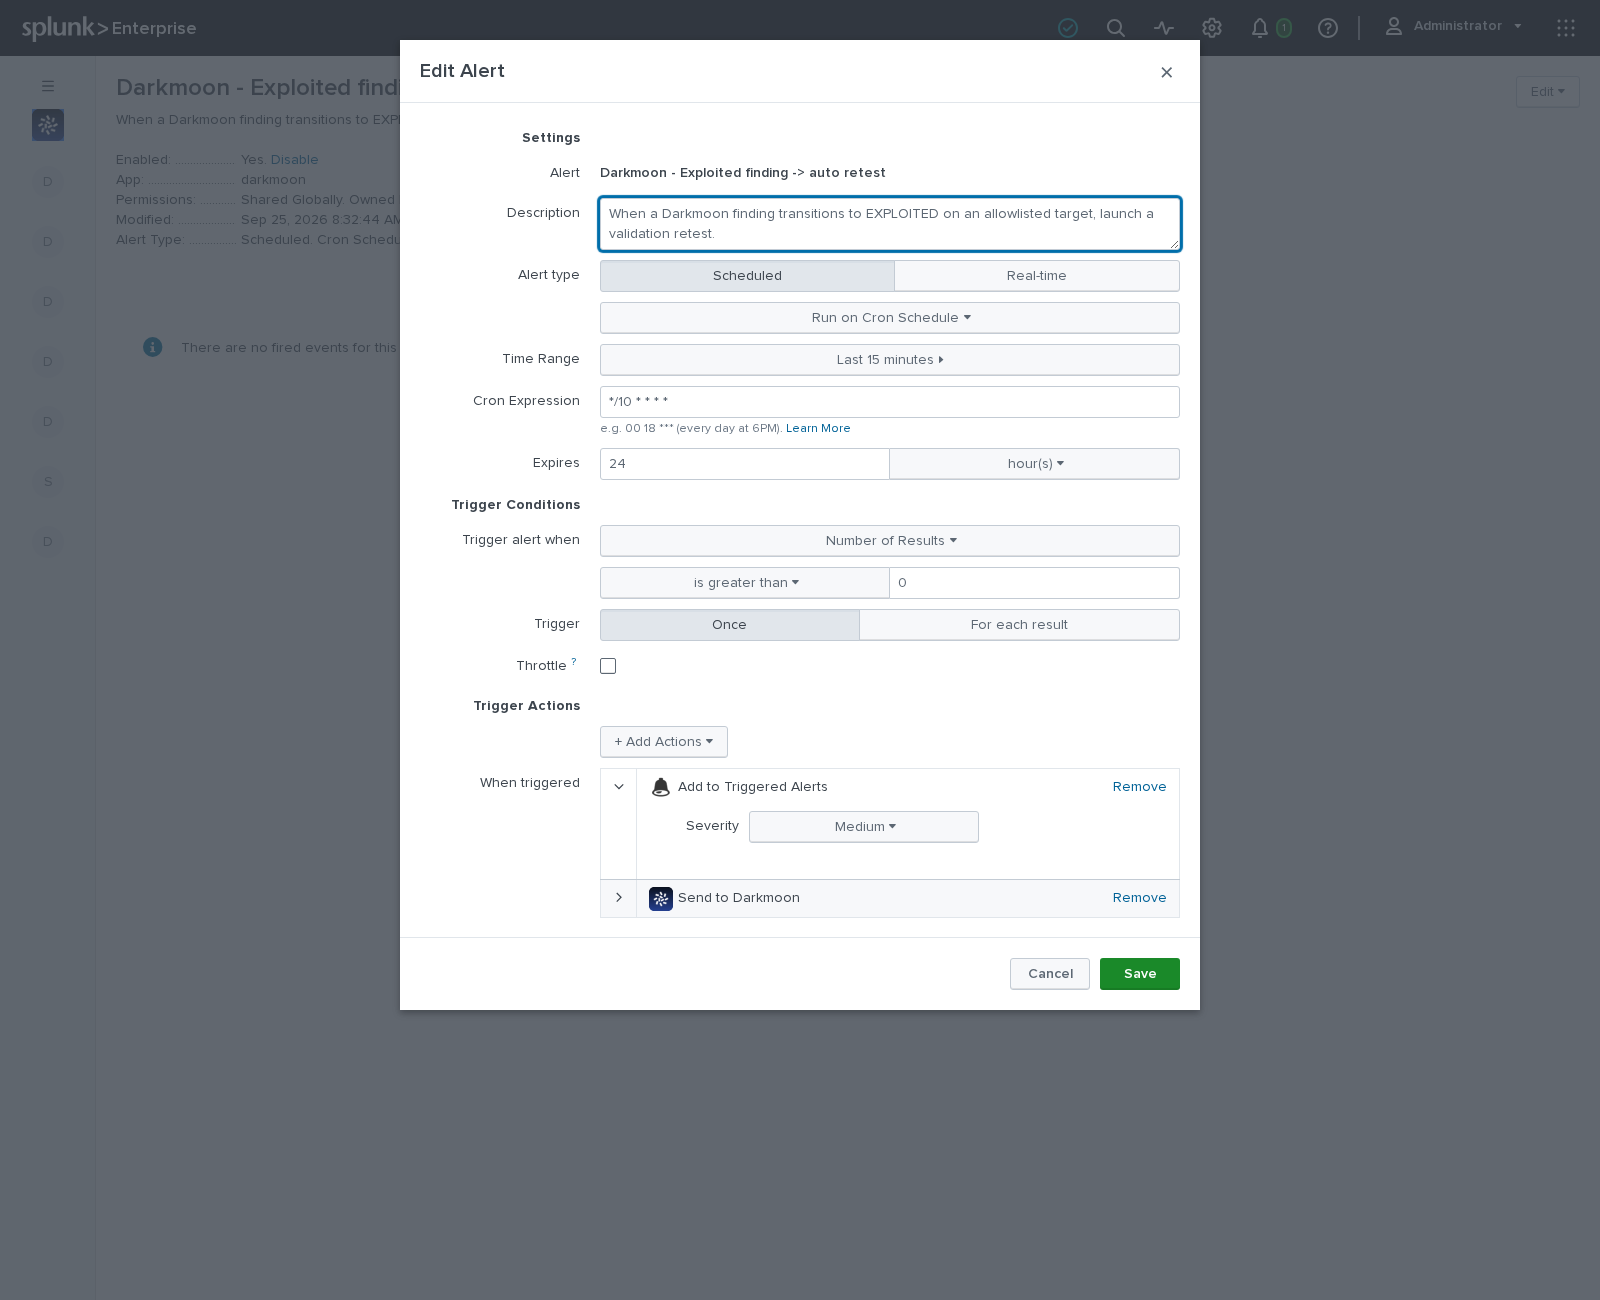
Send to Darkmoon alert action — the offensive-validation loop wired into a correlation search:
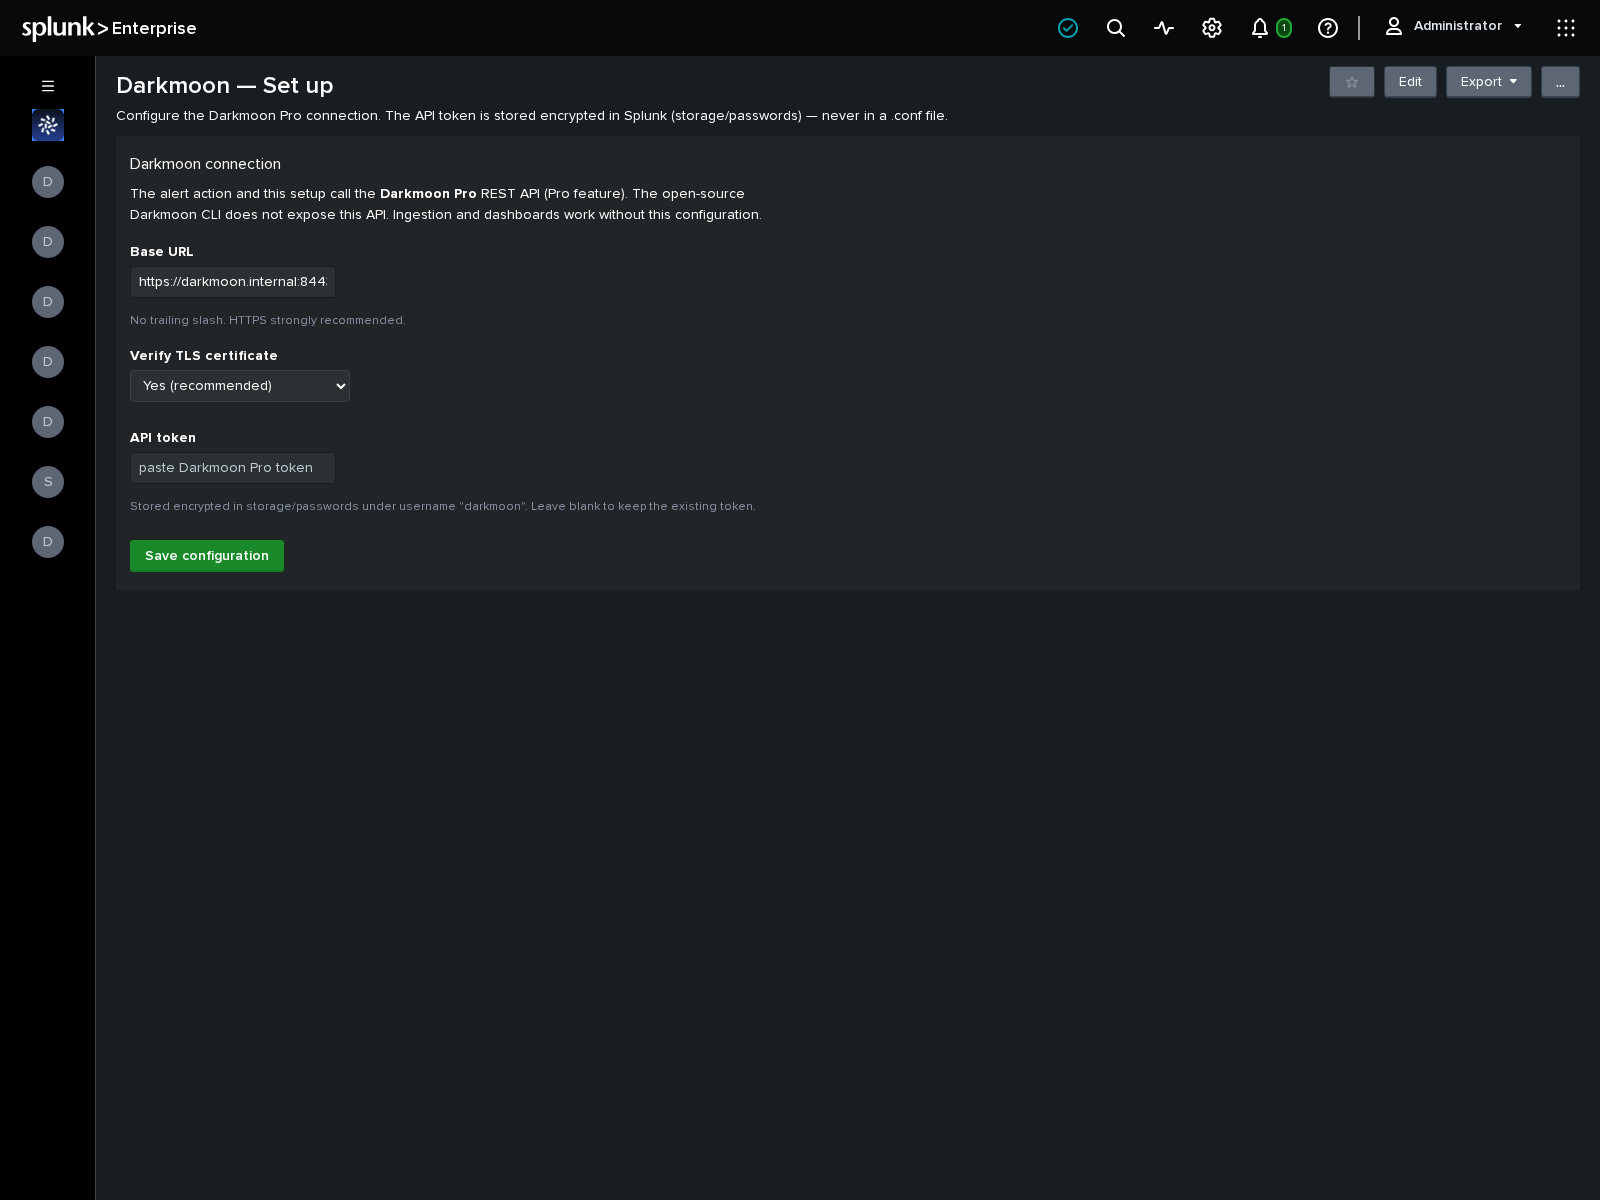
Set up — Darkmoon connection; the API token is stored encrypted in storage/passwords:
- Download the
.spl/.tar.gzfrom Releases and upload it via Apps → Manage Apps → Install app from file. Once approved (app 9875, pending), you will also be able to install it from Splunkbase: Apps → Find More Apps → search "Darkmoon Pentest" → Install. - Restart Splunk if prompted.
- Open Manage Apps → Darkmoon Pentest → Set up to store the Darkmoon Pro base URL and API token (needed only for the alert action; ingestion and dashboards work without it).
- Settings → Data inputs → HTTP Event Collector → New Token. Name it
darkmoon, set the app context to Darkmoon Pentest, optionally route to an index nameddarkmoon. - Point a producer at
https://<splunk>:8088/services/collector/event:- Pro (recommended): register a Darkmoon webhook (
format=splunk_hec) targeting the HEC URL. The Darkmoon dispatcher formats safe, HMAC-signed envelopes for you. - Anyone: run the bundled
forwarder/darkmoon-to-hec.py.
- Pro (recommended): register a Darkmoon webhook (
- Events land as
darkmoon:campaign,darkmoon:finding,darkmoon:retest,darkmoon:pr, parsed and CIM-aligned (Vulnerabilities data model) by this app.
export DARKMOON_TOKEN=...        # Pro bearer (poll mode)
export SPLUNK_HEC_TOKEN=...      # HEC token
# poll the Pro REST API and ship safe events:
python3 forwarder/darkmoon-to-hec.py \
  --rest-url https://darkmoon.internal:8443 \
  --hec-url  https://splunk.internal:8088/services/collector/event
# or from a JSON export, or dry-run to stdout:
python3 forwarder/darkmoon-to-hec.py --export export.json --stdout
See forwarder/README.md for the full flag list and the export shape.
Send to Darkmoon triggers a Darkmoon retest/campaign from a correlation search — an
unauthenticated-by-default destructive capability on the Darkmoon side, so it is hard-secured:
- Target allowlist — only hosts in
lookups/darkmoon_targets.csvcan ever be sent; everything else is refused (no arbitrary / out-of-scope scanning, ever). - Safe-harbor — non-destructive profile enforced unless a target row explicitly opts in.
- Auth — the Darkmoon token is read at runtime from Splunk
storage/passwordsvia the session key; it is never stored in a.conf, log or dashboard. - Rate limiting — token bucket (max launches/hour), hard-capped in the script.
- TLS verification — on by default; non-HTTPS Darkmoon URLs are refused while verify is on.
- Untrusted input — any target derived from a result row is validated against a strict host/IP regex before use (prevents command/SSRF injection).
- Dry-run ON by default — nothing launches until you set
dry_run=0.
Three example correlation searches ship disabled in savedsearches.conf
(exploited→retest, critical-spike→campaign, regression→retest). Review, restrict the allowlist,
then enable.
Ingestion and dashboards work with any Darkmoon edition that can emit events. The alert action and the setup page call the Darkmoon Pro REST API and are Pro-only — the open-source Darkmoon CLI does not expose that API. This app never presents the Pro dashboard/API features as open source.
| Splunk Enterprise | 9.0+ (tested on the latest splunk/splunk Docker image) |
| Splunk Cloud | Yes (AppInspect precert + cloud tags clean) |
| Platform | Platform-independent (Simple XML dashboards, stdlib Python) |
| CIM | Vulnerabilities 5.x field mapping |
| Python | Alert action runs on Splunk's bundled Python 3 (python.version=python3, python.required=3.13) |
Real, reproducible tests live in test/:
# offline (no Docker): safe-field allowlist + alert-action guards + mock launch
python3 test/gen_synthetic.py
python3 forwarder/darkmoon-to-hec.py --export test/fixtures/darkmoon-export.json --stdout
python3 test/test_alert_action.py
python3 test/test_mock_launch.py

# full E2E against REAL Splunk in Docker (parses, dashboards render, no leaks)
cd test && docker compose up -d splunk       # then wait for healthy
bash test/run_e2e.sh
AppInspect (Splunkbase cloud vetting mirrors this):
pip install splunk-appinspect
splunk-appinspect inspect darkmoon --mode precert
Latest local run: 0 errors, 0 failures, 0 future-failures (2 ignorable warnings — the SplunkJS
telemetry notice and the generic "python file present" notice). Report: docs/appinspect-precert.json.
MIT © 2026 ASC-IT (SARL) / Darkmoon. See LICENSE.